 ISPolitical
App description
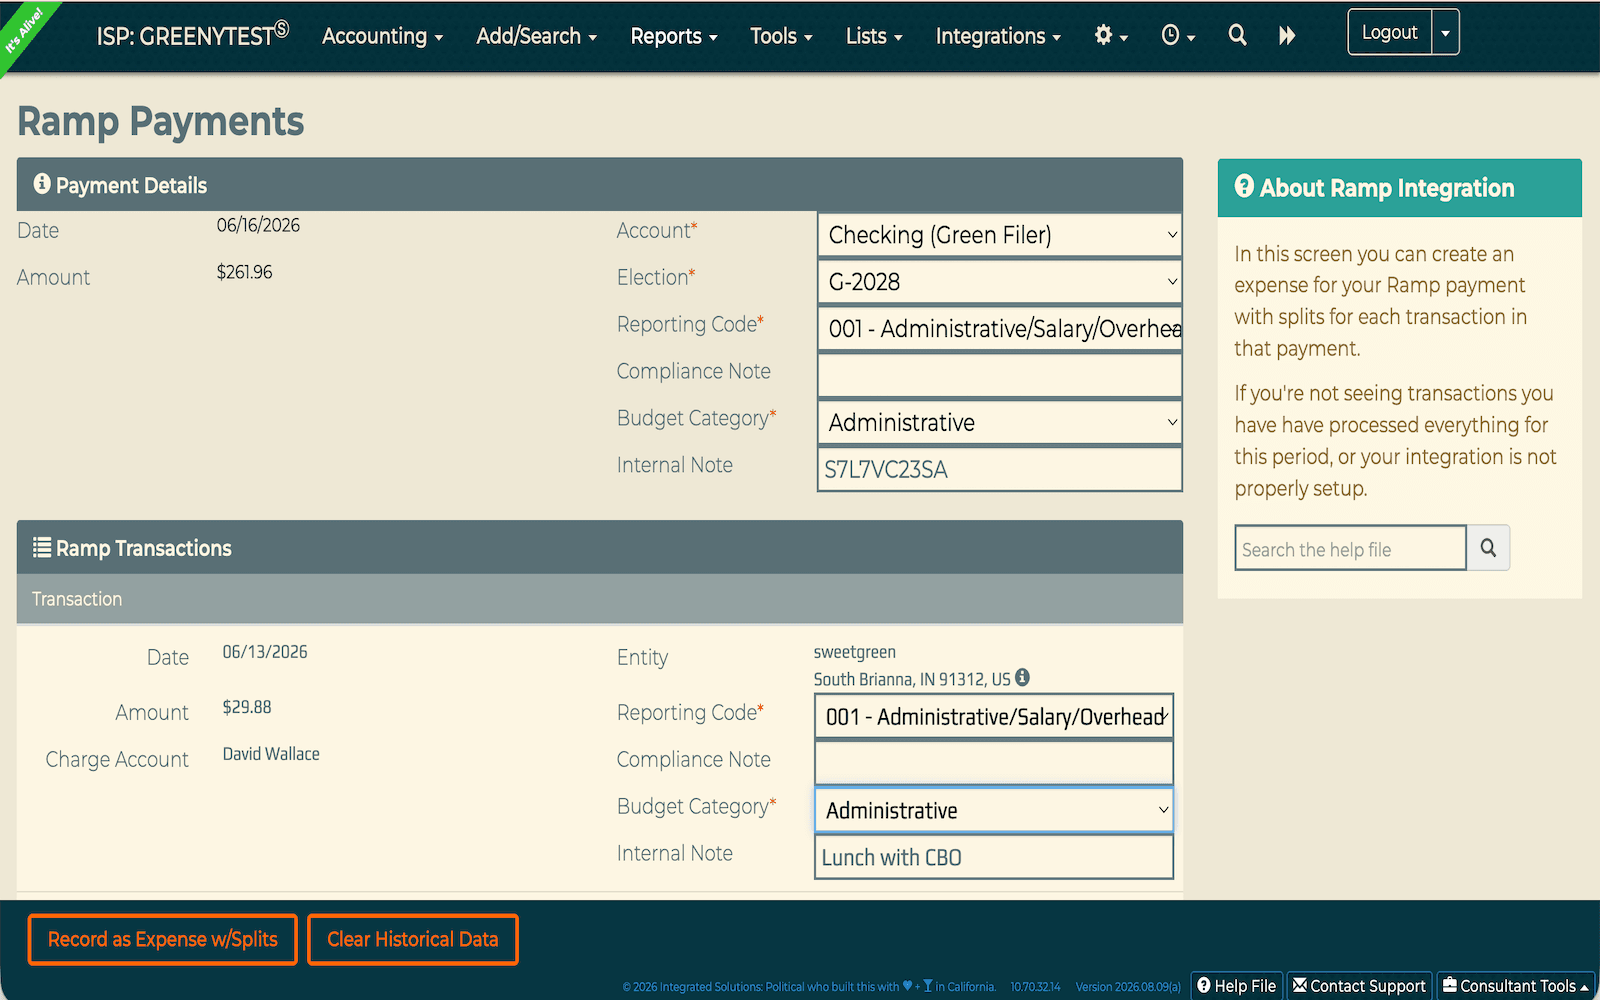
Connect Ramp to ISPolitical to turn card spend into clean, categorized, and compliant political accounting. Fast. Automatically bring Ramp expenses into ISP, reduce manual data entry, and keep your reporting accurate and audit-ready.
Security and compliance
Employees have access for support purposes. Access is limited to appropriate roles (ex: Support team).
Overview
The vast majority of information stored in ISP exists to support legally required campaign finance disclosure rules. In most cases, that information is expected to be disclosed publicly through required filings or public reporting processes.
Because most ISP data is generally public or intended for public disclosure, ISP’s retention policy is based on the relatively low risk of storing that data compared with systems that primarily store highly sensitive private information. ISP’s goal is to store as little highly sensitive information as possible.
Due to regulatory requirements and ISP’s goal of providing the highest level of service to customers, ISP retains customer data for 20 years.
Core rules
- Retain customer data for 20 years to support regulatory obligations, historical reporting needs, and customer service.
- Recognize that most ISP data supports legally required disclosures and will generally be made public.
- Keep only the data needed for a legitimate business, support, legal, compliance, security, or recovery purpose.
- Minimize collection and storage of highly sensitive information whenever possible.
- Do not keep unnecessary duplicate copies of client data.
- Store client data only in approved company systems.
- Delete temporary files, exports, restored databases, and local copies when the work is complete.
- Use anonymized, redacted, synthetic, or limited data whenever possible in development and testing.
- Important decisions and client-specific details should be recorded in durable systems like JitBit or Notion.
Production backups
Current Azure SQL backup retention:
EnvironmentPoint-in-time restoreLong-term retentionLive Azure SQL Database1 dayWeekly: 2 weeks; Monthly: 3 months; Yearly: keep 2 weeks for 1 yearLive replica7 daysNot setDev Azure SQL Database1 dayNot set
Backups are for continuity, disaster recovery, and limited recovery from accidental deletion, corruption, defects, or infrastructure failure. They are not intended to be an indefinite archive.
Temporary and support data
Temporary restored databases, exports, imports, troubleshooting files, and QA/support copies should be used only for the specific task that required them.
Delete them when:
- The data has been extracted or validated and
- The support, import, export, QA, or troubleshooting task is complete and
- The data is no longer needed for comparison or recovery
Sensitive data
Minimize exposure of sensitive data. Unless approved by a manager, do not place the following into AI tools or unapproved third-party systems:
- Client confidential information
- PII
- Financial or legal data
- Contracts or legal documents
- Proprietary strategy
Use summarized, generic, anonymized, or redacted information whenever possible.
Exceptions
Legal, contractual, agency, audit, litigation, or leadership requirements may require data to be kept longer or handled differently. Exceptions should be documented and approved by Jose Dias, Ben Katz, or another designated ISP leader.
https://ispolitical.com/security-policy/
.
Penetrtion Test
Discover more integrations
Ramp integrates with all your existing software so you can manage your business with ease—from one place.