 Raisi Ramp Onboarding
App description
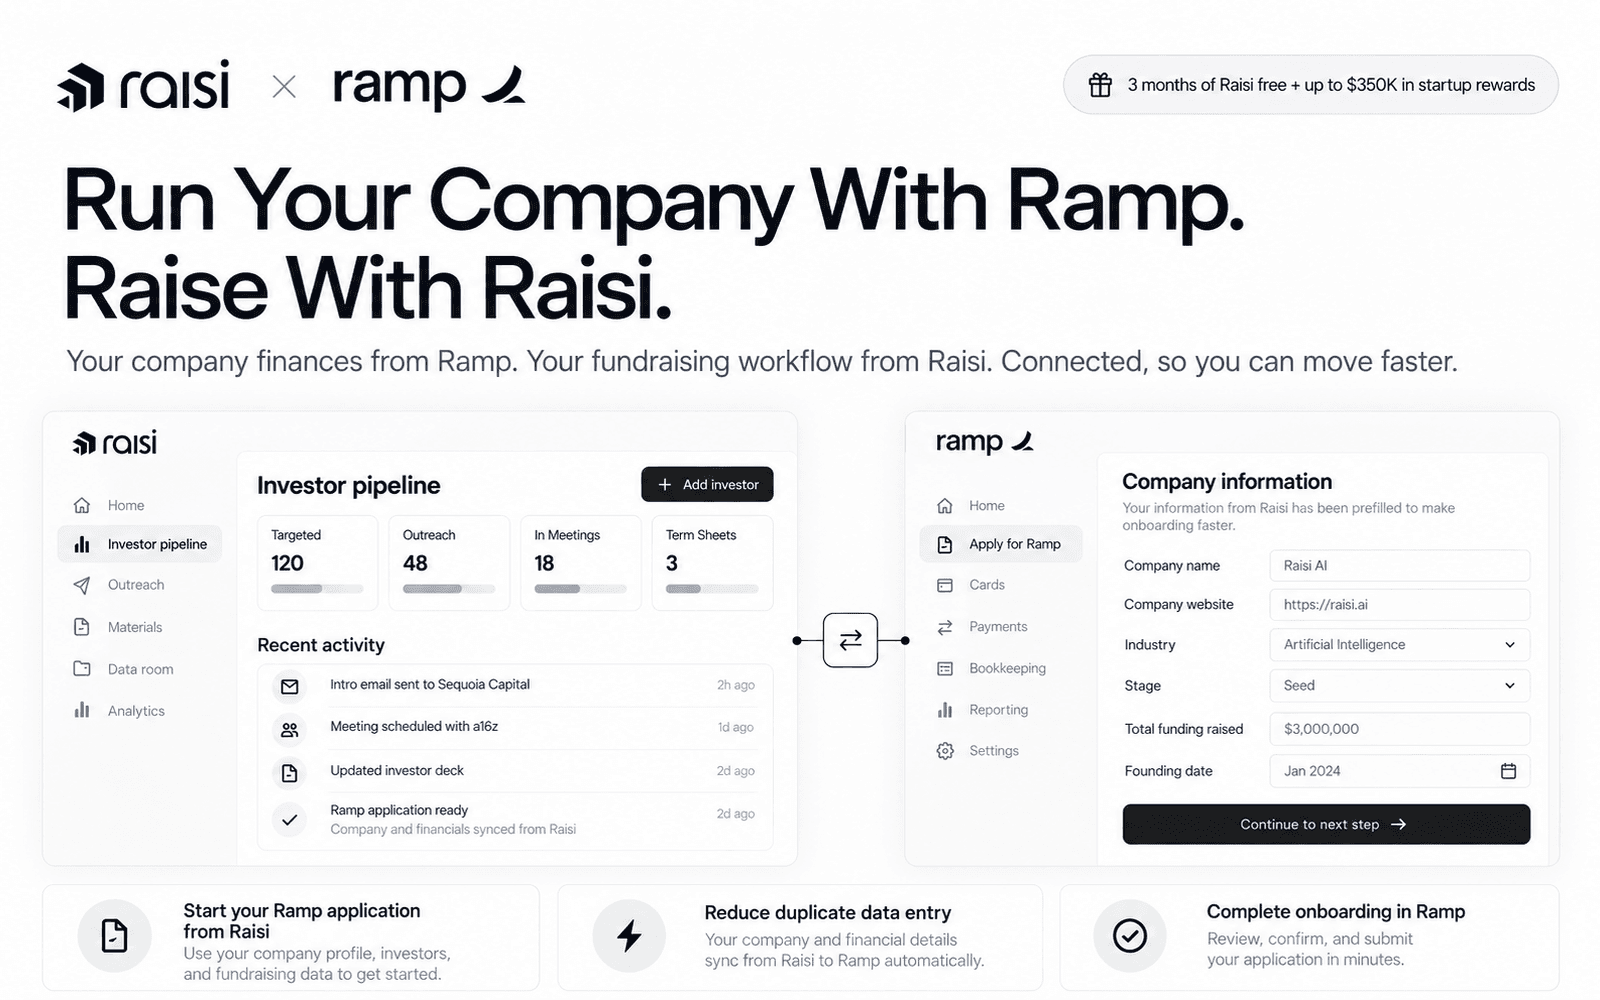
Raisi is an AI-powered fundraising platform that helps founders prepare for and execute their raise, from investor matching and outreach to pipeline management, meetings, and fundraising materials.
The Raisi + Ramp integration makes it easier for founders to set up the financial infrastructure behind their company while they raise capital. Eligible Raisi customers can begin their Ramp application directly through Raisi using company information they've already provided, reducing duplicate data entry and creating a smoother onboarding experience.
Once the application is created, founders continue through Ramp's onboarding experience to provide any additional information, complete required verification, and finish their application.
Raisi does not manage Ramp accounts, cards, transactions, or spend on behalf of customers. Ramp remains the system of record for the Ramp application and account.
Security and compliance
No. Ramp integration data is not broadly accessible to all Raisi employees. Access is limited to authorized engineering and operations personnel who need it for integration support, incident response, or debugging, under role-based and least-privilege access controls, with MFA required for privileged accounts. Customer-facing access in-product is limited to authenticated users within the relevant company workspace. Access is logged, and Raisi does not use this data for unrelated purposes.
Ramp integration records are retained for the life of the related Raisi company account so we can show application status, avoid duplicate applications, and support attribution. Records may be deleted or returned within 30 days of a written customer request to close/delete their account, except where retention is required for legal, security, dispute, or audit purposes. OAuth tokens are retained only as needed to maintain and update application status and may be rotated or invalidated when no longer required. Broader retention practices are described in our Privacy Policy (Section 6.1): https://www.raisi.ai/privacy-policy
https://www.raisi.ai/privacy-policy
.
Raisi does not currently maintain SOC 2 Type II, ISO 27001, or PCI certification. Our security practices are described in our Privacy Policy (Section 6.2) and include encryption in transit and at rest, role-based and least-privilege access, MFA for privileged accounts, logging, vendor diligence, and regular vulnerability review.
Discover more integrations
Ramp integrates with all your existing software so you can manage your business with ease—from one place.